February 17, 2022, Posted by Absolute Destruction
Last Updated:
Key Takeaways
- Patient records must be disposed of securely to stay compliant with PHIPA and PIPEDA.
- Cross-cut shredding and secure document destruction help protect personal health information.
- A clear retention policy ensures records are kept only as long as required.
- Trusted shredding companies in Toronto can provide compliant patient records disposal.
- ePHI also needs secure destruction to prevent privacy breaches.
Everyone has patient records, some dating back to before birth. Because it is so common, people take it for granted. But there is a lot of identifiable health information, so health records need proper disposal.
Hospitals have been criticized before for sending old medical records of patients out for recycling instead of using shredding companies in Toronto. Anyone can get information about patients without making an access request.
If unauthorized people access medical records because of improper disposal, it could lead to potential privacy liabilities. Below are the legalities of protecting patient records.
Legislation Concerning Patient Records in Canada
The personal health information contained in patients' medical records deserves protection from unauthorized access. Under Canadian law, institutions and health professionals who fail to keep their patients' trust may be legally liable.
The following laws protect the integrity of sensitive and identifiable personal information, including patient records. At the same time, these Ontario laws provide legal ways for their disclosure for acceptable reasons, including proper ways to do document shredding in Burlington.
Personal Health Information Protection Act
The Personal Health Information Protection Act of 2004, or PHIPA sets out the rules that apply to all health information custodians in Ontario for collecting, using, and disclosing identifiable health information. The act must take reasonable steps to protect that information from loss, theft, and unauthorized use. In case of a breach, the custodian must inform the affected individuals of that fact.
An affected individual may choose to lodge a complaint with the Information and Privacy Commissioner, an appointee under the Freedom of Information and Protection of Privacy Act. If it results in a conviction, the offending party may be liable to pay up to $10,000 in damages for mental anguish to the affected person.
Privacy Act
The Privacy Act encompasses health and medical records held by the Ontario government. Information includes details of medical treatment received by patients paid for under the Ontario Health Insurance Plan, the province's healthcare plan. Anyone can make an access request with the Ministry of Health and Long-Term Care under limited circumstances. These include:
- The patient consents
- The court orders it
- The government passes a law, such as in the case of infectious diseases
PIPEDA Act
The Personal Information Protection and Electronic Documents Act (PIPEDA) is a federal law for privacy protections in private-sector organizations and setting out the rules for the way businesses handle personal health information. Under limited circumstances, this could apply to personal health information.
Institutions and organizations regulated under PIPEDA must get the concerned party's consent before collecting, using, or disclosing their personal data.
Designing Your Practice's Document Retention and Destruction Framework
Managing historical medical charts can quickly turn into an administrative challenge for busy healthcare facilities. Practice managers often ask: When can we legally clean out the file storage room? To protect your clinic from regulatory risks, your team must implement a formal, written document retention policy alongside an automated retention schedule that carefully maps out file lifecycles from creation to secure final disposal.
Standard Retention Windows for Canadian Patient Files
According to standard medical record retention guidelines, general adult records must be preserved for a specified retention period of at least 10 years from the date of the last entry. For pediatric care, files must stay active for at least 10 years after the minor reaches the age of majority.
Mitigating Risk with Closed Storage and Access Controls
Because of state-specific retention rules and civil litigation windows under local limitations acts, many Canadian clinics choose to archive patient records for up to 15 years to stay completely safe. While these records are stored throughout their legal lifecycle, administrators must use strict restricted access zones and heavy secure containers or locked consoles to deter internal data breaches.
Pre-Destruction Asset Tracking and Team Accountability
All physical inventory movements must be logged within your facility’s maintenance logs before executing any secure document destruction process. Overlooking these steps can result in significant legal liabilities, which is why regular workforce training and clear written policies are mandatory for every onboarding employee. To ensure your office operations align perfectly with provincial frameworks, management teams should establish their file lifecycles using the rules for retention, transfer, and disposal.
Evaluating Enterprise Vendors for Secure Document Shredding
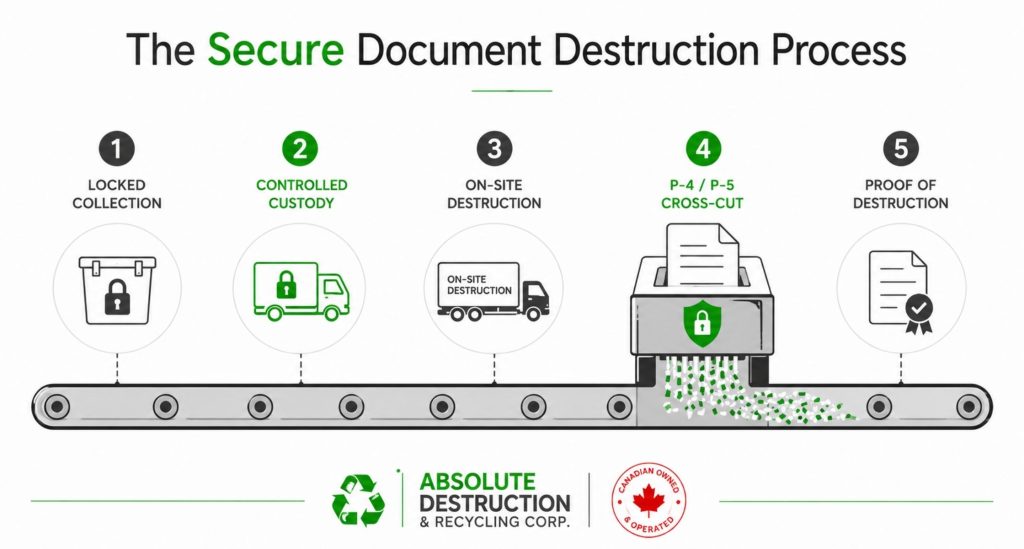
When it comes to the final step of document disposal, medical operations cannot treat patient data like standard commercial recycling. Simply discarding intact charts into an open recycling container invites severe data breaches and regulatory fines. Protecting your facility requires a systematic, secure collection routine and carefully choosing and managing shredding services that can seamlessly verify compliance with privacy laws.
Chain-of-Custody Protocols and Legal Agreements
When evaluating a third-party shredding provider, first verify their operational chain-of-custody protocol. Your management team needs to know exactly who handles the files from the moment they are dropped into your clinic’s locked bins until they are completely destroyed. Your business relationship with the vendor must be locked down using a comprehensive business associate agreement that explicitly outlines legal data liabilities.
On-Site Mobile Cross-Cut Destruction Technology
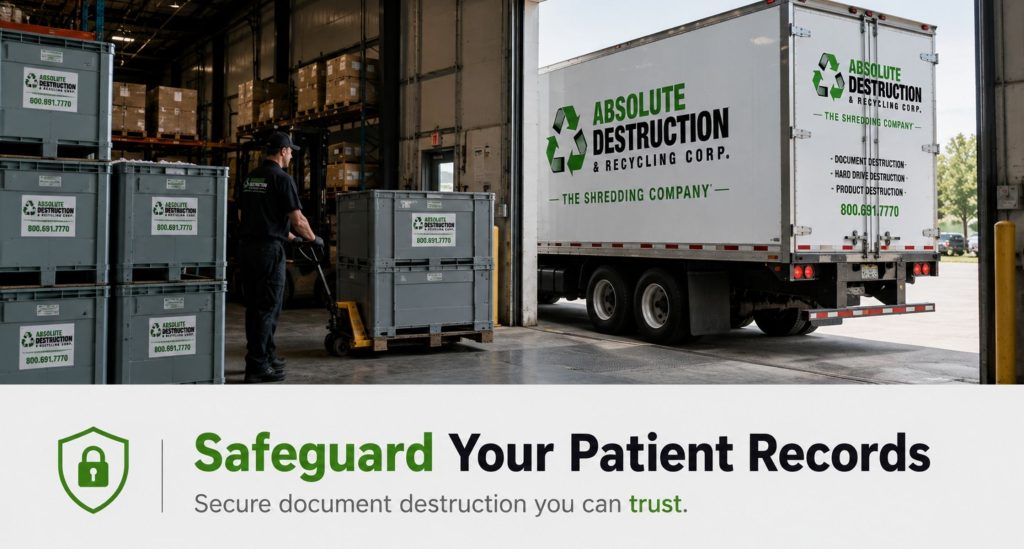
For maximum security, eliminate the transport risks of off-site sorting by insisting on on-site cross-cut shredding right at your facility’s door. Industrial data destruction teams, like the mobile trucks operated by Absolute Destruction, use specialized, heavy-duty HIPAA-compliant shredders that reduce paper files to tiny, unrecognizable particles.
Choosing Industrial Shred Sizes for Data Protection
Always review the vendor’s specific shred size and cut type. To safeguard confidential medical data, look for high-security DIN P-4/P-5 cross-cut metrics rather than simple strip-cut methods. Once your primary secure collection run is finished, you can transition your clinic to a hands-free, scheduled shredding routine—allowing your business to balance day-to-day data safety with an eco-friendly disposal process that diverts clean, shredded paper into local recycling pulp mills. You can cross-reference your vendor policies with the administrative Personal Health Information Protection Act report.
Modernizing Your Digital Media and ePHI Sanitization
Physical paper records are only one piece of the compliance puzzle. Modern clinics run on electronic protected health information (ephi), meaning that every old hard drive, legacy server, out-of-date tablet, and digital medical device in your office represents a massive data liability if left unchecked. Properly executing the disposal of digital medical records requires an updated, comprehensive corporate privacy policy that dictates exactly how retired computer hardware is decommissioned.
The Limitations of Standard Desktop File Deletion
Simply deleting files or formatting a local drive does not erase the underlying information; data recovery tools can easily reconstruct patient records. To achieve true digital safety, your IT security team or data destruction provider must follow the rigorous media sanitization practices outlined in the NIST special publication 800-88.
Understanding the NIST Clear, Purge, and Destroy Framework
This gold-standard security framework categorizes digital device destruction into three defensive methodologies depending on the data risk level:
- Clear: Overwriting logical storage sectors using software commands to block basic keyboard data recovery attempts.
- Purge: Utilizing targeted firmware modifications or a complete cryptographic erase to wipe internal decryption keys, making laboratory-level data recovery impossible.
- Destroy: Completely shredding, crushing, or melting the physical solid-state drives (SSDs), magnetic platters, or memory chips.
Maintaining PHIPA Compliance for Old Medical Devices
Adhering to these verified data workflows shields your medical practice from failing a hipaa breach notification rule audit and ensures your entire team remains aligned with Ontario’s strict PHIPA provisions. Make sure your technical support staff logs all unique device identifiers, executes verified data verification steps, and logs the specific method used before any retired electronics leave your facility. To avoid hidden digital processing blind spots, reference the defensive practices for safeguarding personal health information.
Navigating the Compliance File Audit: Proof of Destruction
If the Information and Privacy Commissioner of Ontario opens an unexpected inquiry into your practice’s data management habits, verbal explanations are legally insufficient. Your administration must be able to present undeniable, documented proof to protect your organization from severe fines and reputational damage. Maintaining a rigorous system for documentation and proof of destruction ensures you are always ready for a surprise compliance check.
Certificates of Destruction as Your Primary Legal Shield
Every time a mobile shredding truck visits your office, they must provide an official certificate of destruction. This document acts as your primary legal shield, explicitly itemizing your clinic's collected container IDs, the exact destruction method used, and a verified operator signature confirming the work was completed on-site.
Chronological Tracking and Vendor Visibility Tools
To build an airtight compliance file, your office manager should maintain chronological destruction logs that detail what files were destroyed and when, without exposing sensitive patient names. To maximize your operational security, look for enterprise-level vendor features like GPS-enabled real-time tracking
or physical witness options that let your clinic staff watch the shredding take place live on a built-in truck monitor.
Securing Contractual Audit Rights for Long-Term Safety
Finally, ensure your business associate agreement grants your organization explicit audit rights to inspect the processing facility. All generated certificates, transport logs, and compliance records must be held securely in your files for the entire duration of your organization's legal retention period. For a real-world case study on the financial liabilities associated with unmonitored discarding errors, review the regulatory decision regarding ensuring secure disposal of health records.
Medical Disclaimer: The information provided in this article is for general educational and informational purposes only and does not constitute formal legal or professional compliance advice. Privacy regulations, CPSO bylaws, and IPC interpretations can evolve; always consult a qualified privacy attorney or an official compliance officer to review your specific organizational destruction workflows.
Safeguard Your Patient Records
Personal privacy laws in Canada and specific provinces spell out the responsibilities of private institutions and public health services for securing a patient's information and health records. To avoid loss of trust and legal liability, you should only disclose the appropriate amount of information dictated by law. That includes ensuring any patient records for disposal are appropriately handled.
Take the first step in protecting patient records with the help of Absolute Destruction. Contact us today and learn more about our services.
FAQs on the Legalities of Protecting Patient Records
Can you sue a doctor for breaching patient confidentiality?
There is no tort law for breaching patient confidentiality in Canada. But a patient in Ontario can lodge a complaint with the Information and Privacy Commissioner, an appointee under the Freedom of Information and Protection of Privacy Act. If the Commissioner deems there has been actual harm to the patient from the breach, the doctor may be liable for damages up to $10,000.
An individual found to be in violation of PHIPA may be fined up to $200,000 plus a year in prison. An institution may be liable for up to $1,000,000.
How do I keep my medical records private?
You can keep your medical records confidential by directing your physician or healthcare professional to keep them so.
Before you sign anything, check the fine print to ensure there are no clauses that will allow the custodian to disclose any information. Ask for a copy of your patient records so you can see what they contain.
If you believe there has been any breach in the privacy of your medical records, lodge a complaint to the appropriate authorities based on your province.
When can a doctor break confidentiality in Canada?
A doctor can break confidentiality in Canada in the following circumstances:
- They are required by law
- They obtained informed consent from the patient
- A court orders it
How should a healthcare organization choose a shredding provider?
Healthcare organizations should choose a shredding provider that offers secure collection, clear handling procedures, an appropriate destruction method, and documented proof of service. Ask whether the provider supplies locked bins or consoles, conducts on-site destruction, and issues a Certificate of Destruction. Absolute Destruction offers regularly scheduled console service, one-time on-site shredding, and secure locked bins for confidential documents. A written service agreement should also define confidentiality expectations and responsibilities for protecting personal health information.
Are locked bins useful for protecting patient records?
Yes. Locked bins and security consoles help prevent unauthorized access while staff collect outdated patient records, intake forms, billing documents, or other confidential paperwork. They give employees one designated place to deposit documents awaiting secure destruction rather than leaving them in open recycling containers or desks. Absolute Destruction provides locked bins and security consoles that can remain at an office and be serviced at regular intervals. Restrict access to these containers and train staff on what materials belong inside.
Is on-site shredding appropriate for medical records?
On-site shredding is appropriate for medical records because confidential paper records are collected and destroyed at the healthcare organization’s premises. This reduces the time documents spend in transit after collection and allows staff to observe the secure destruction process when needed. Absolute Destruction uses a mobile shredding truck to collect and immediately shred confidential documents on-site. Ontario guidance recommends cross-cut or micro-cut shredding so personal health information cannot reasonably be reconstructed.
What documentation should be kept after medical records are destroyed?
A Certificate of Destruction should be retained with internal destruction logs and the organization’s records-management documentation. The file should identify the service date, types or categories of records destroyed, destruction method, authorized personnel, and the applicable retention schedule. This documentation can help demonstrate that the organization followed its written policies and used a secure document destruction process. Absolute Destruction provides a Certificate of Destruction after on-site shredding is complete.
How should electronic medical records and devices be disposed of?
Electronic medical records must be securely destroyed or sanitized before computers, hard drives, mobile devices, USB drives, backup media, or other storage devices are reused, recycled, or discarded. Deleting files alone may not make personal health information unrecoverable. The appropriate method depends on the device and whether the media will be reused, but it must protect against unauthorized access. Absolute Destruction provides commercial electronic data destruction for hard drives, laptops, tablets, phones, flash drives, and backup media.
Does PHIPA require the secure disposal of patient records?
Yes. Ontario’s Personal Health Information Protection Act requires health information custodians to take reasonable steps to protect personal health information and to securely dispose of records in their custody or control. Secure disposal should make reconstruction or unauthorized recovery of the information not reasonably foreseeable. Before authorizing destruction, organizations should verify that the required retention period has ended and that no legal, regulatory, professional, or litigation-hold requirement requires the records to be retained.
How can scheduled shredding help prevent privacy breaches?
Scheduled shredding creates a consistent, controlled process for managing confidential paperwork as it becomes eligible for destruction. Employees deposit documents in locked bins or security consoles, and trained technicians collect and shred the materials at an agreed interval. This reduces the risk of patient records being misplaced, mixed with regular recycling, or accessed by unauthorized individuals. Absolute Destruction offers regularly scheduled console service and one-time shredding for organizations with different disposal needs.
What belongs in a patient-record retention and destruction policy?
A patient-record retention and destruction policy should state how long each record category is retained, who may authorize destruction, and how paper and electronic records are secured before disposal. It should also cover locked containers, restricted access, employee training, internal destruction logs, vendor responsibilities, and Certificates of Destruction. The policy should be reviewed regularly because retention obligations can vary by healthcare profession, record type, and applicable Ontario requirements. PIPEDA guidance also expects organizations to have procedures for secure disposal.
What are the risks of improperly disposing of patient records?
Improper disposal can expose personal health information to unauthorized access, privacy breaches, identity theft, medical fraud, complaints, regulatory scrutiny, and reputational harm. Throwing patient files into ordinary recycling or disposing of electronic devices without secure data destruction can leave sensitive information accessible. If a healthcare organization discovers a breach, it should act immediately to contain the incident, assess the information involved, document its response, and meet any PHIPA notification and reporting obligations.